Analysis tools / Defending the answer
Compliance analysis
“What does the audit trail show, framework by framework?”
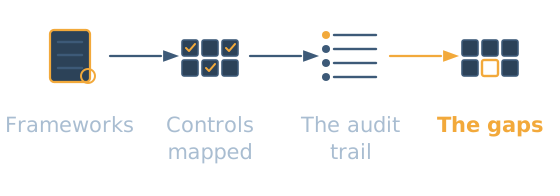
Compliance work fails in a predictable place. The policies exist, the controls are described, and then somebody asks for the evidence that the control was actually operating on the date in question. That is usually the moment a folder of documents turns out not to be the same thing as a record.
The discipline
Three questions, in order. What are we exposed to, which means the regulations and mandates that actually apply to this system rather than the general list. Where do we stand against each of them, which means control coverage mapped to the specific standard, not a claim of general alignment. And what is missing, which is the gap analysis, and is the only part anybody can act on.
Underneath all three sits the unglamorous requirement: evidence that can be produced on demand, generated as work happens rather than reconstructed afterwards.
How SOSX runs it
The analysis works from SOSX's own record of the work done on a network: the per-network audit database, where every model interaction, document write and compliance event is logged as it happens. It scores that evidence control by control against the governance frameworks SOSX is built to align with, including ISO 27001 and ISO 42001, showing for each control how many audit records support it and when the latest was captured, and it reaches a stated verdict on exposure rather than a hedge.
Alongside the scoring it generates the supporting documents the assessment refers to, including a risk assessment, an agent capability matrix and security mappings. Where a document cannot be generated because the underlying evidence is not there, it says so explicitly rather than producing a confident-looking blank.
What you get
A report with the exposure verdict, control coverage by framework, the audit-trail evidence behind it, the documents generated, the ones that could not be, and the assumptions behind the assessment. It exports to PDF or Word.
It is evidence of how SOSX's own work on your network lines up with those frameworks: alignment, not certification, and not an assessment of your organisation's or your product's compliance. The frameworks themselves, and how SOSX aligns with each, are set out on the compliance frameworks page.
The others in this group
Someone will ask how you know. These are the analyses that answer them.
Risk register
“What could go wrong, and how badly?”
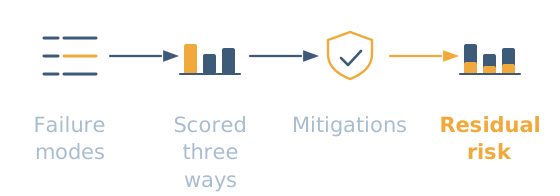
Severity, occurrence and detection in the FMEA style, scored before and after the mitigations you propose.
SWOT
“Where are we strong, and where are we exposed?”
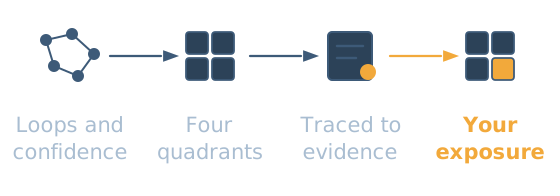
The familiar four quadrants, but built out of the model's loops and confidence levels rather than a workshop's memory.
Governance analysis
“Who decides this, and who has to be told?”
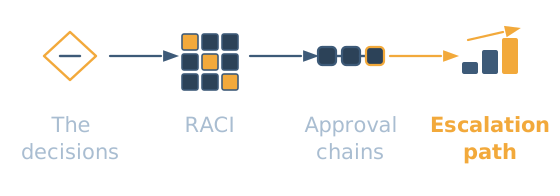
Decision rights, accountability and escalation paths, as a RACI matrix and the approval chains behind it.
Network quality critique
“How much should we trust this model?”
Centrality, single points of failure, orphans and coverage gaps, scored, with the fixes ranked by what they buy you.
Or see all the analysis tools. If you would rather we built the model and ran them for you, that is our system research, build and analysis service.