Videos · 1:11
SOSX and compliance
Compliance built in: SOSX is built against the frameworks an enterprise review tests, and produces evidence as it runs.
Transcript
Compliance is a strong part of the SOSX story, though not in the direction people expect. SOSX does not audit your systems. It was built against the frameworks an enterprise review holds an AI system to, so it goes into a security review ready.
Said plainly: SOSX aligns with these frameworks and produces evidence for them. Nobody certifies you but your auditor. That evidence is produced as the platform runs, not written up afterwards.
Every AI interaction is audit-logged. Every claim cites a catalogued source. The stages that decide the model pass a human approval gate, and an automatic build is held by review gates it cannot clear on its own.
So when an oversight body asks how an analysis was produced, the answer is an artefact: the sources, the approval trail and the audit log, assembled in hours rather than weeks. And SOSX builds claims, arguments and evidence into assurance cases, ready for a gate review. If your compliance documentation is manual, perpetually stale and rebuilt framework by framework, bring us a real question from your own estate, and watch SOSX work it.
More videos
 SOSX, explained
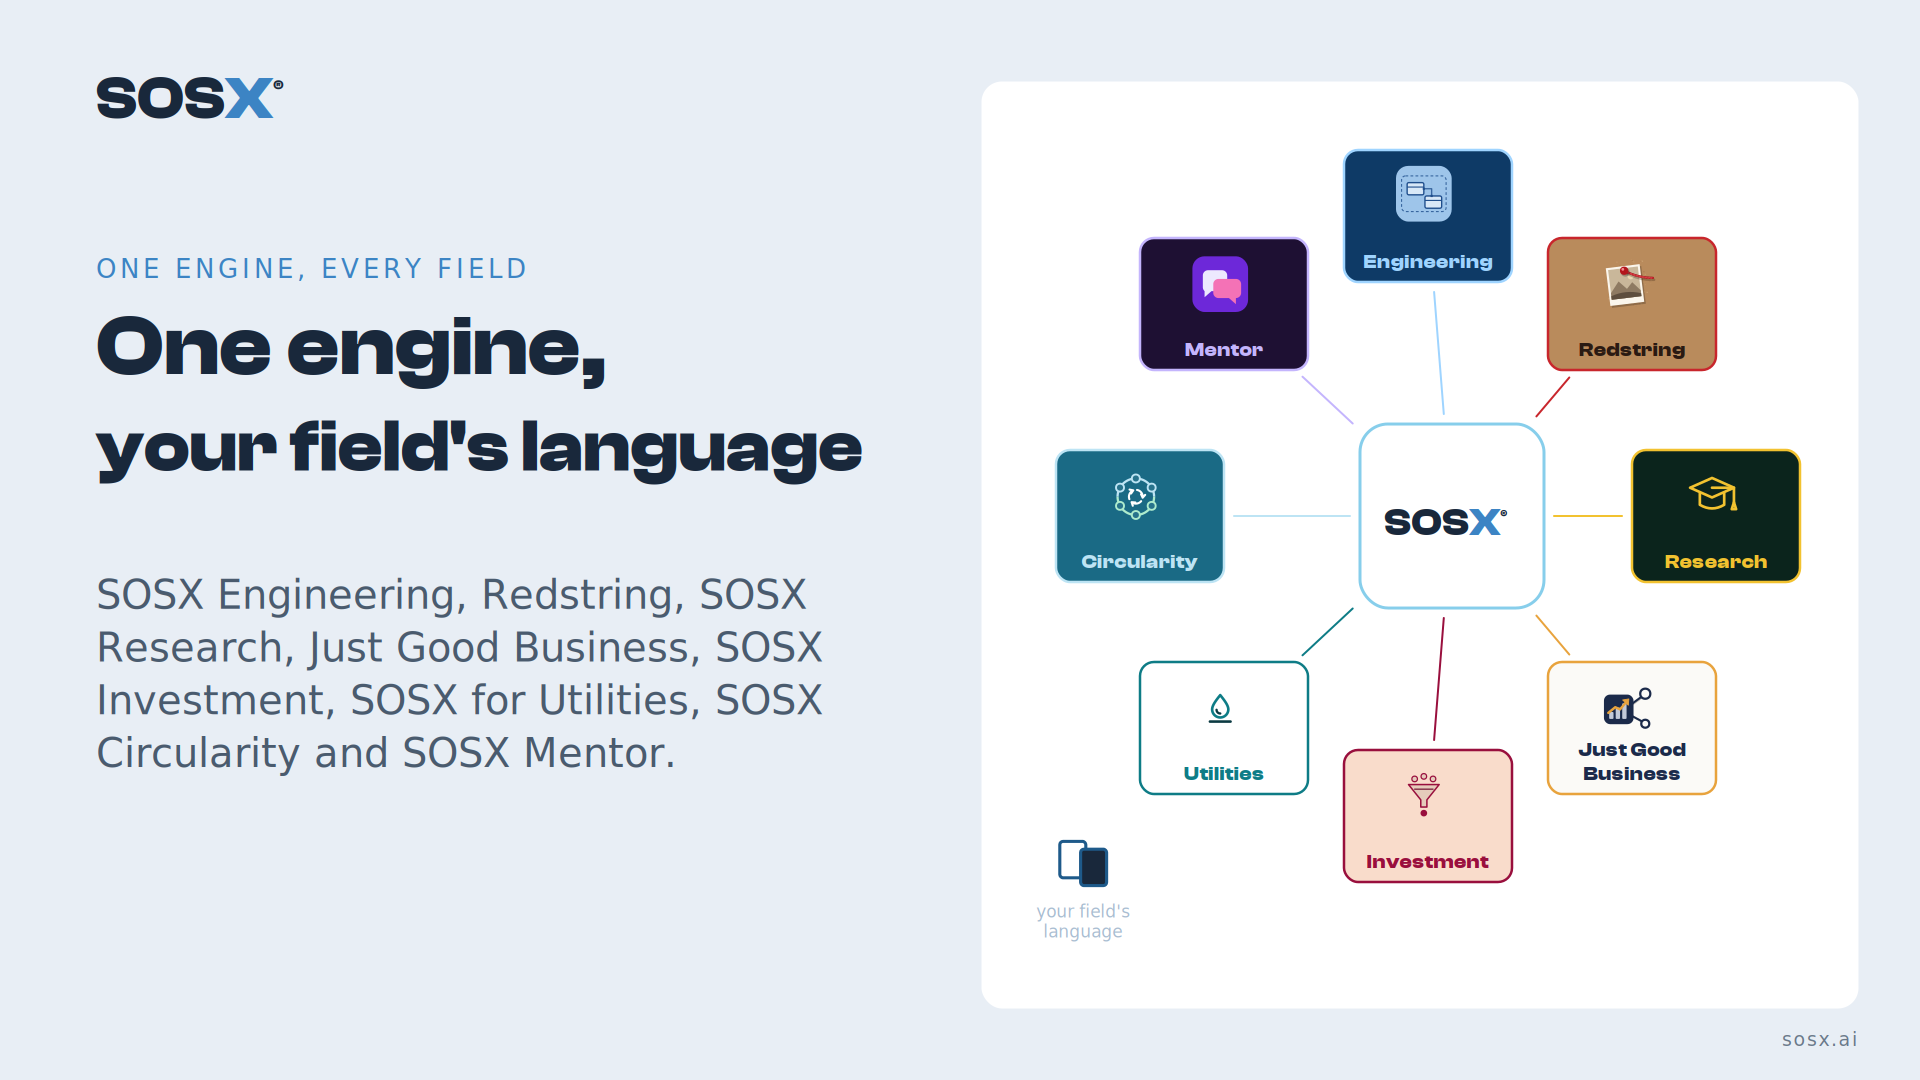 SOSX and its products
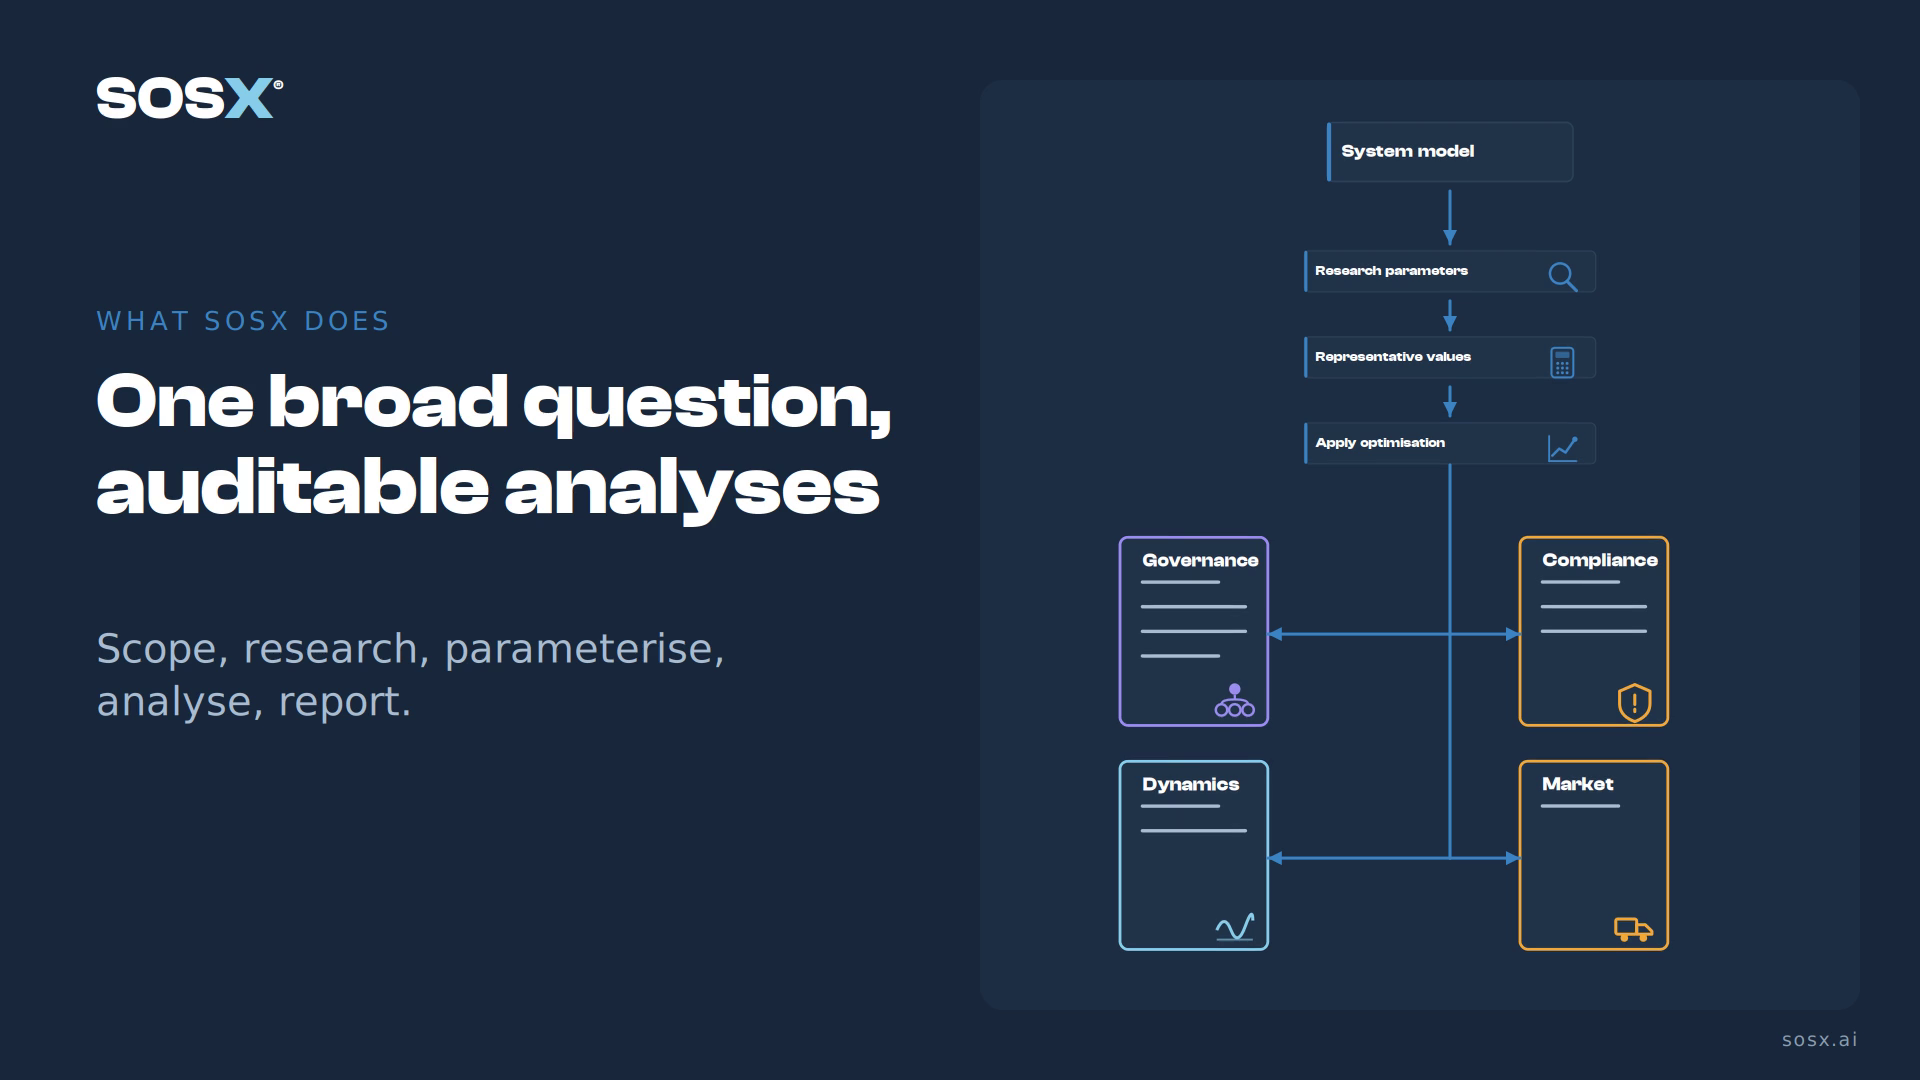 How SOSX works
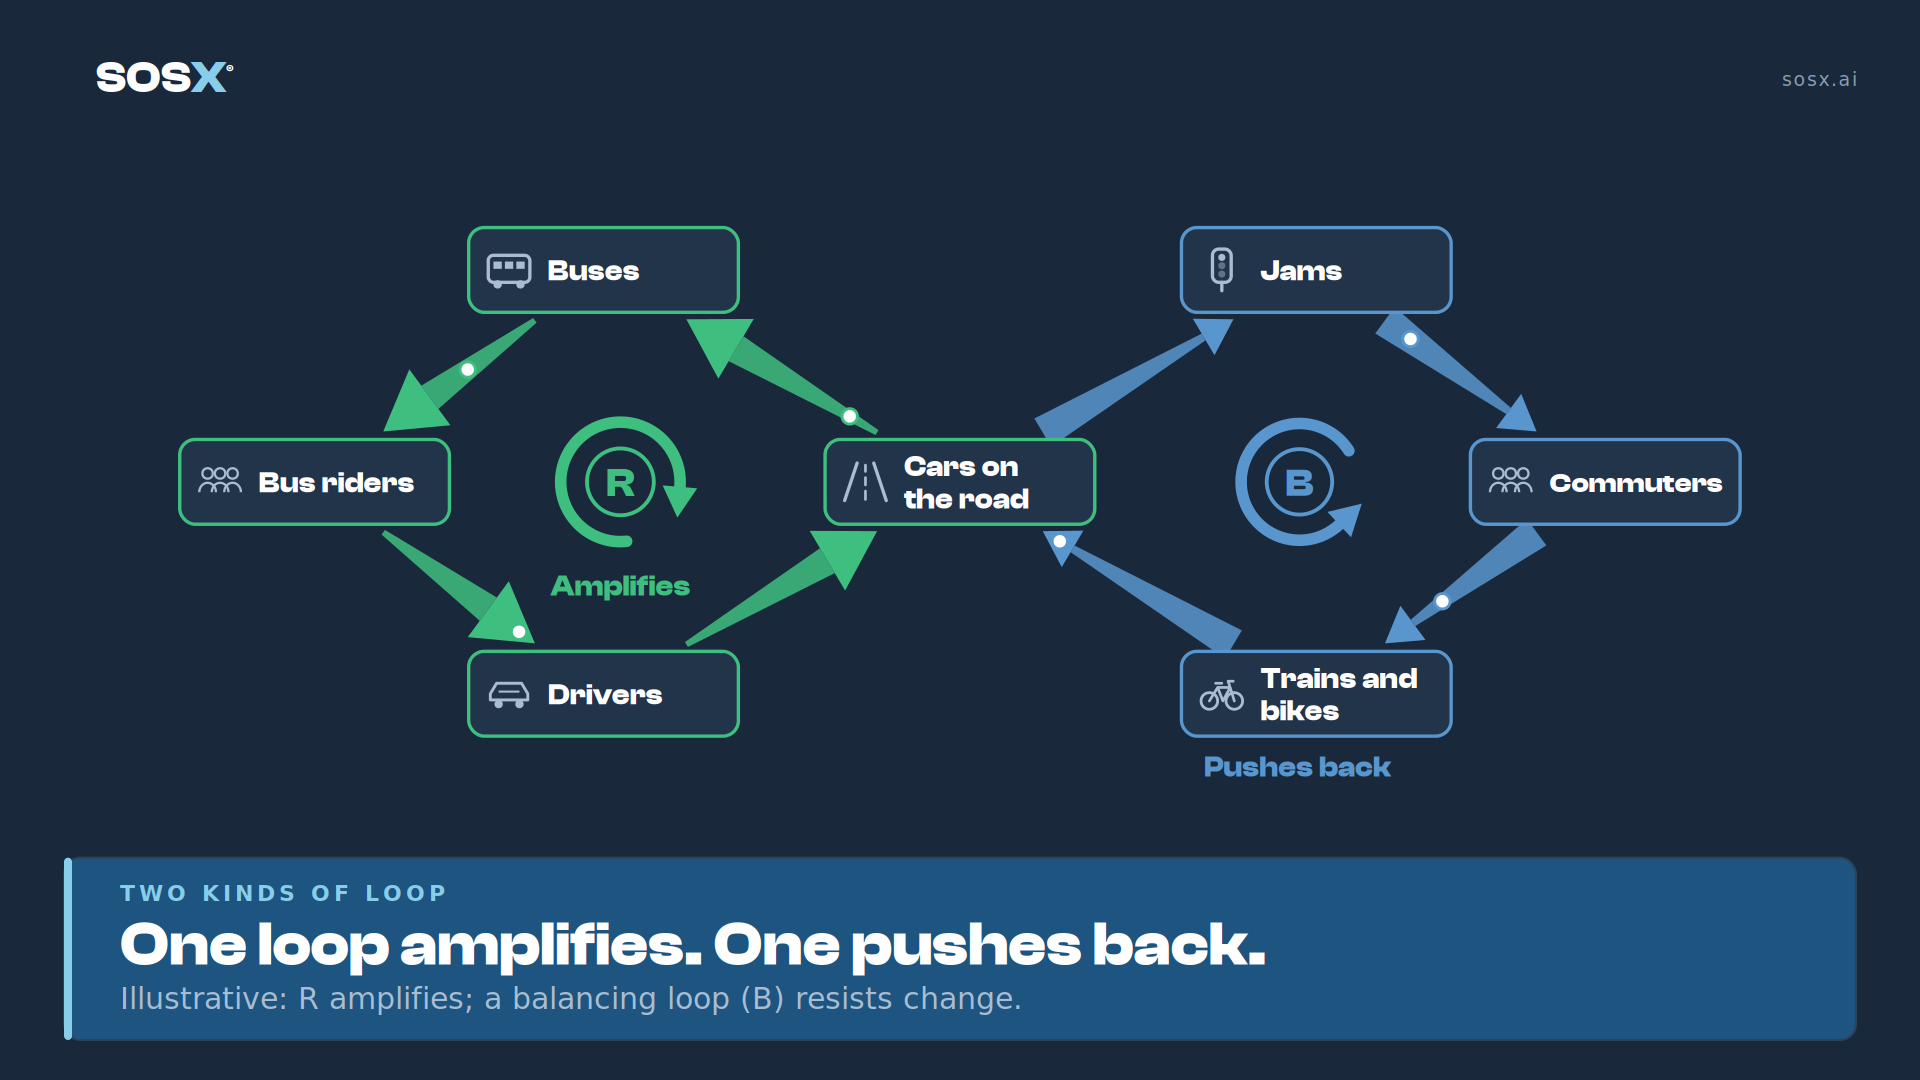 City traffic as a systems map
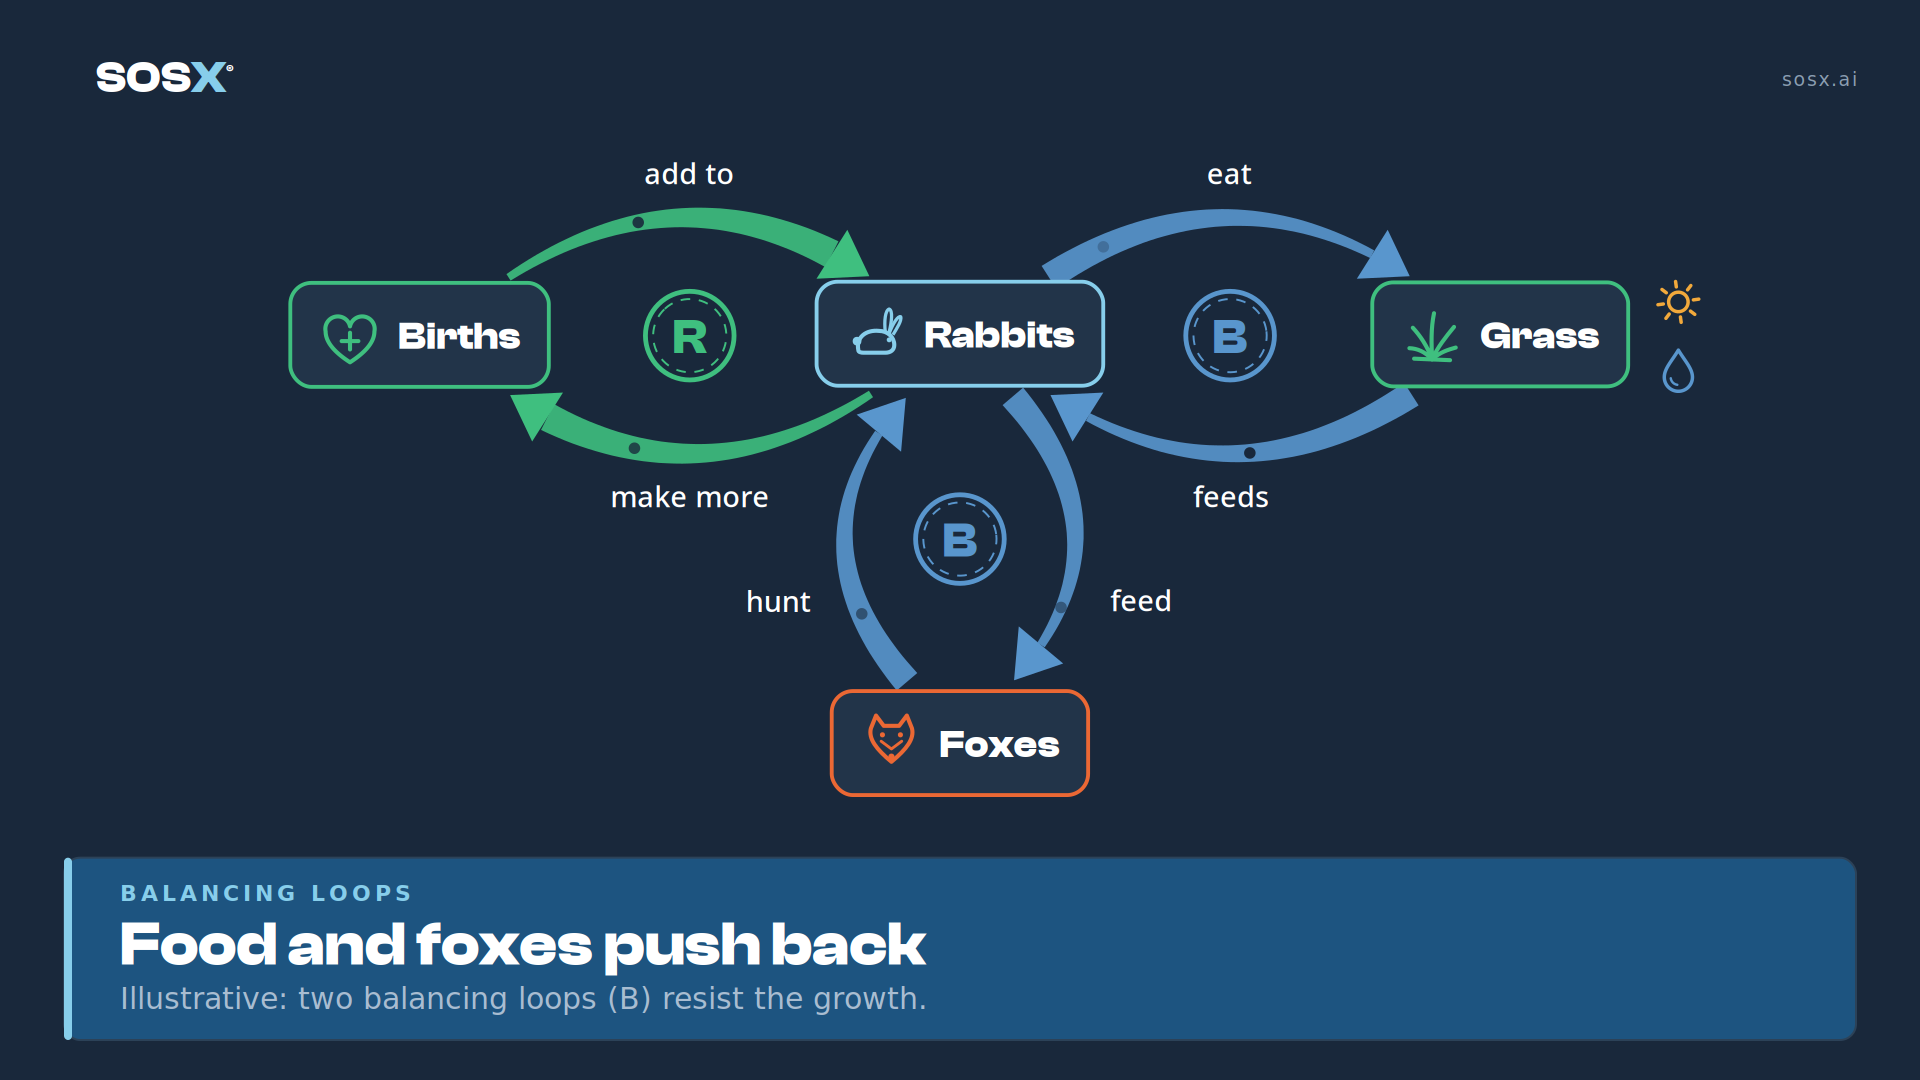 An ecosystem as a systems map
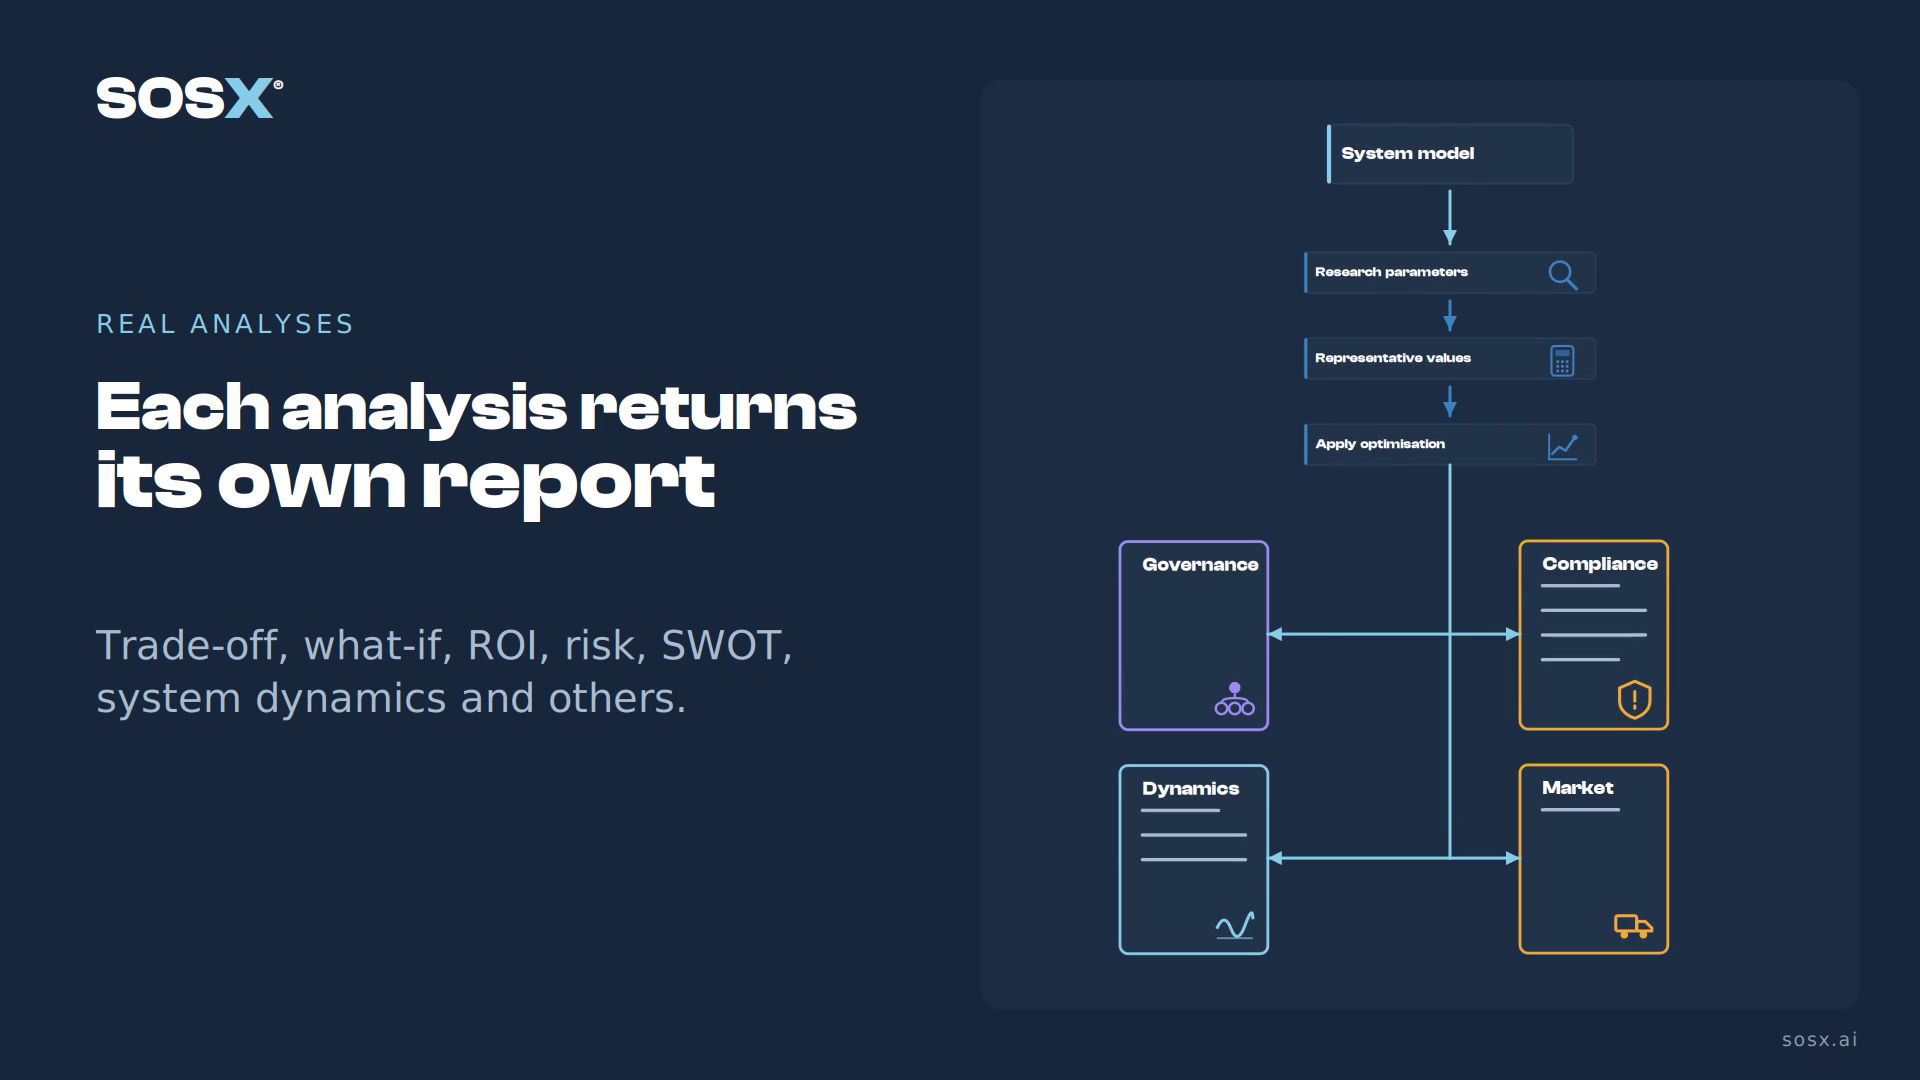 The SOSX analyses
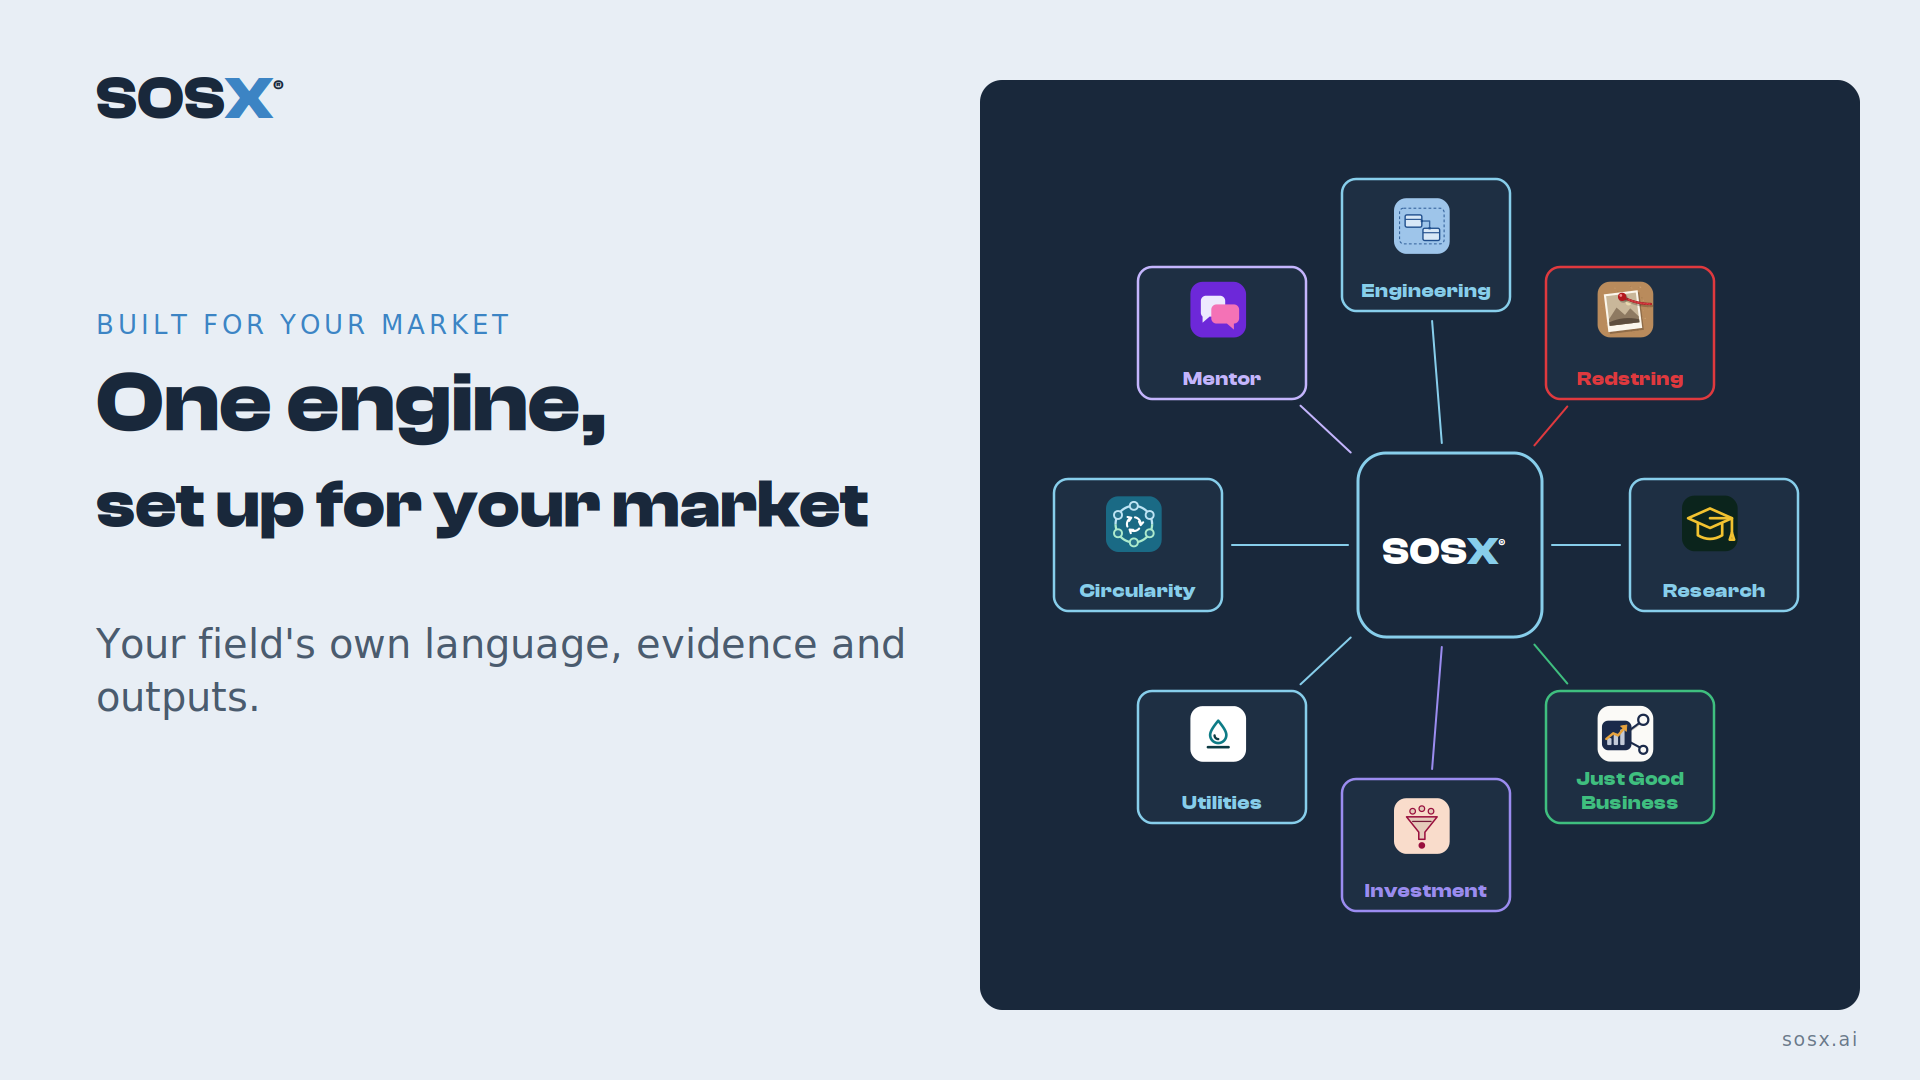 The SOSX editions
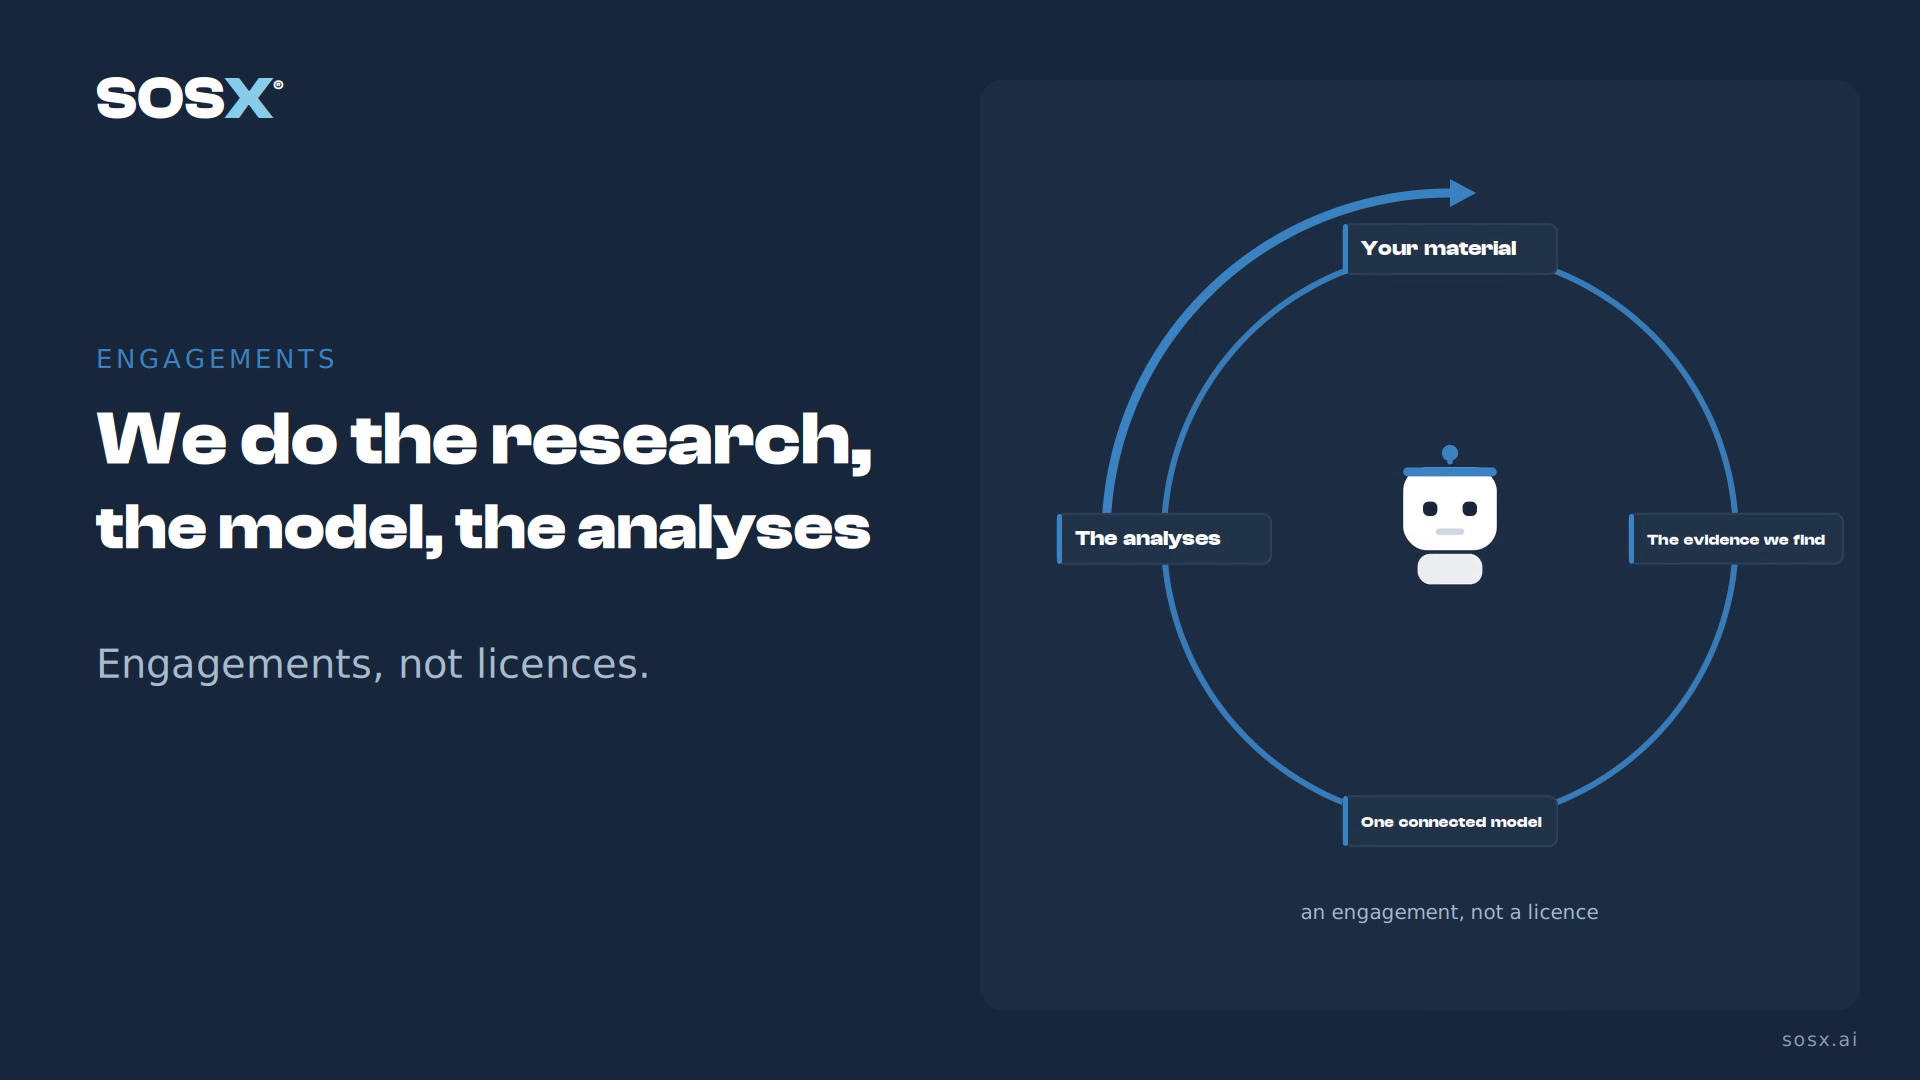 SOSX services
 The SOSX book series
 Why SOSX exists
 Talk to us
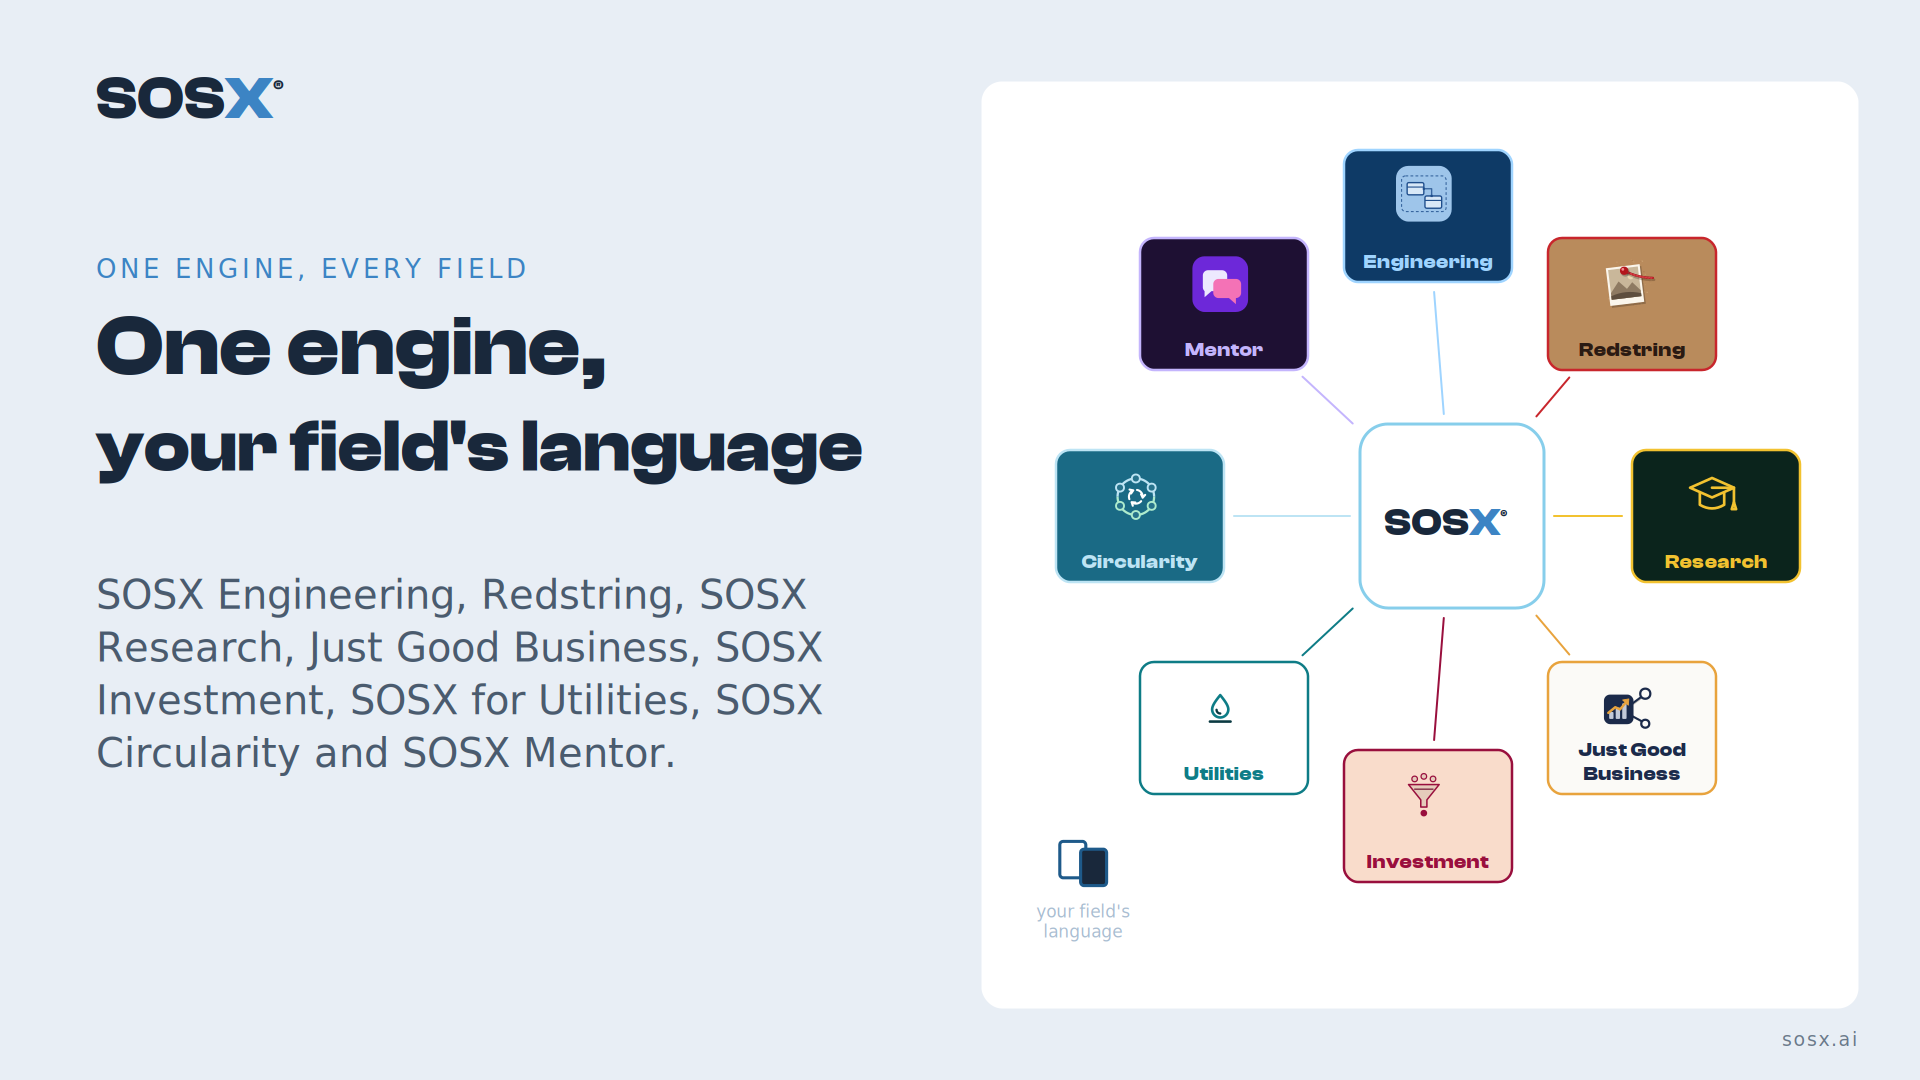
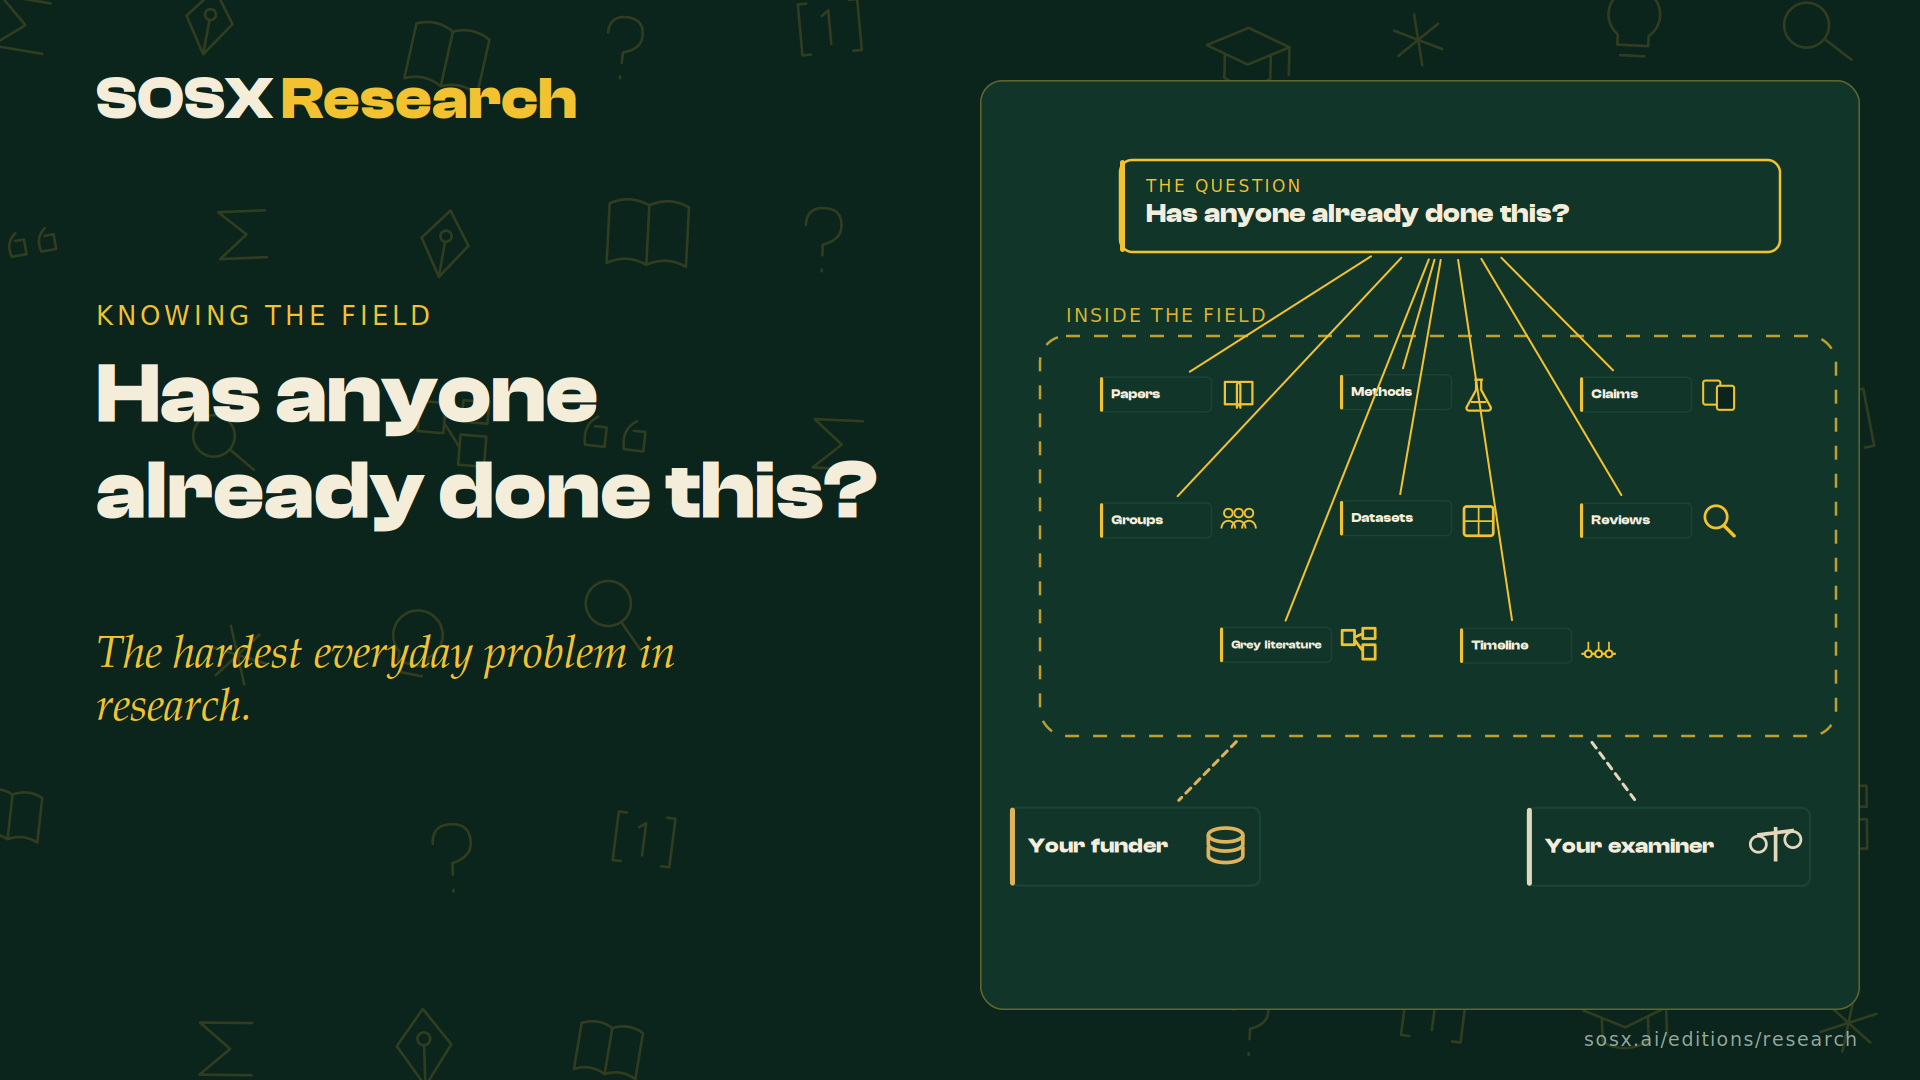 SOSX Research: research support
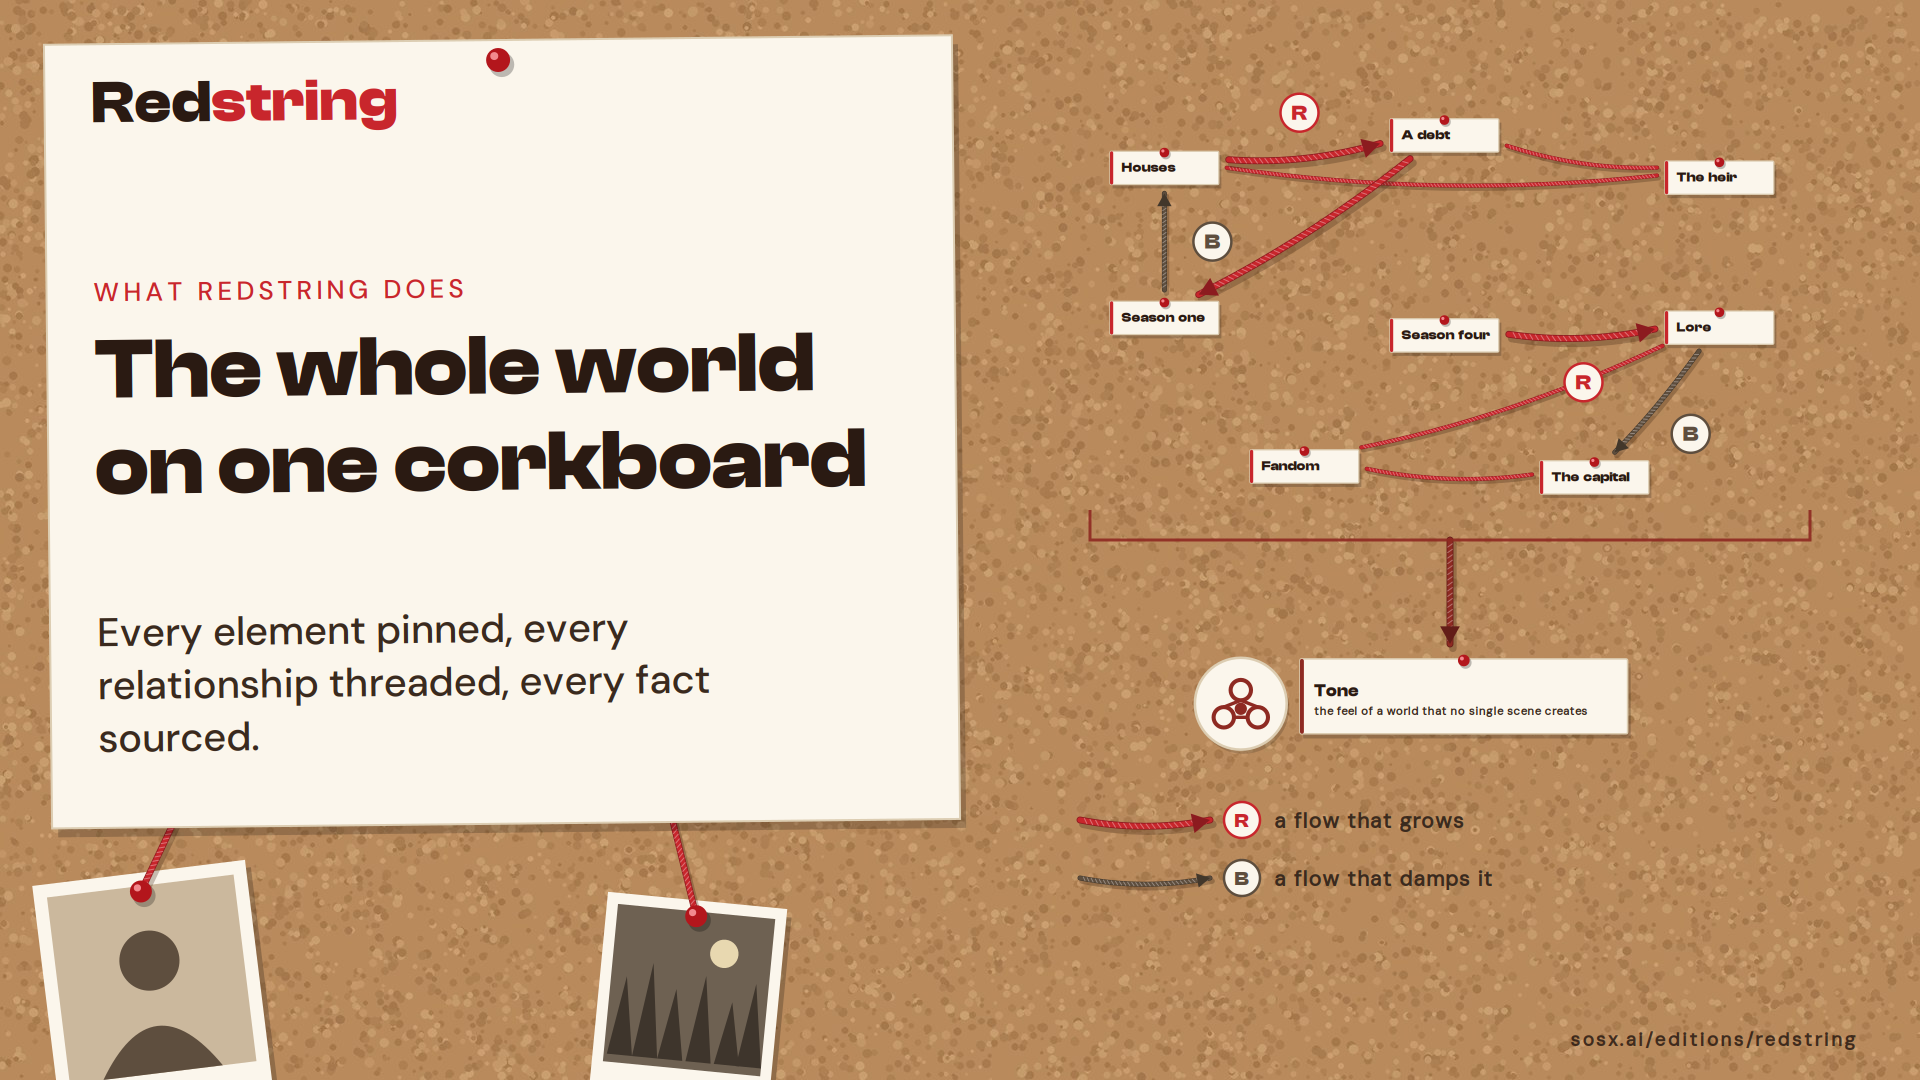 Redstring: story worlds that hold together
 SOSX Engineering
 Redstring
 SOSX Research
 Just Good Business
 SOSX Investment
 SOSX for Utilities
 SOSX Circularity
 SOSX Mentor
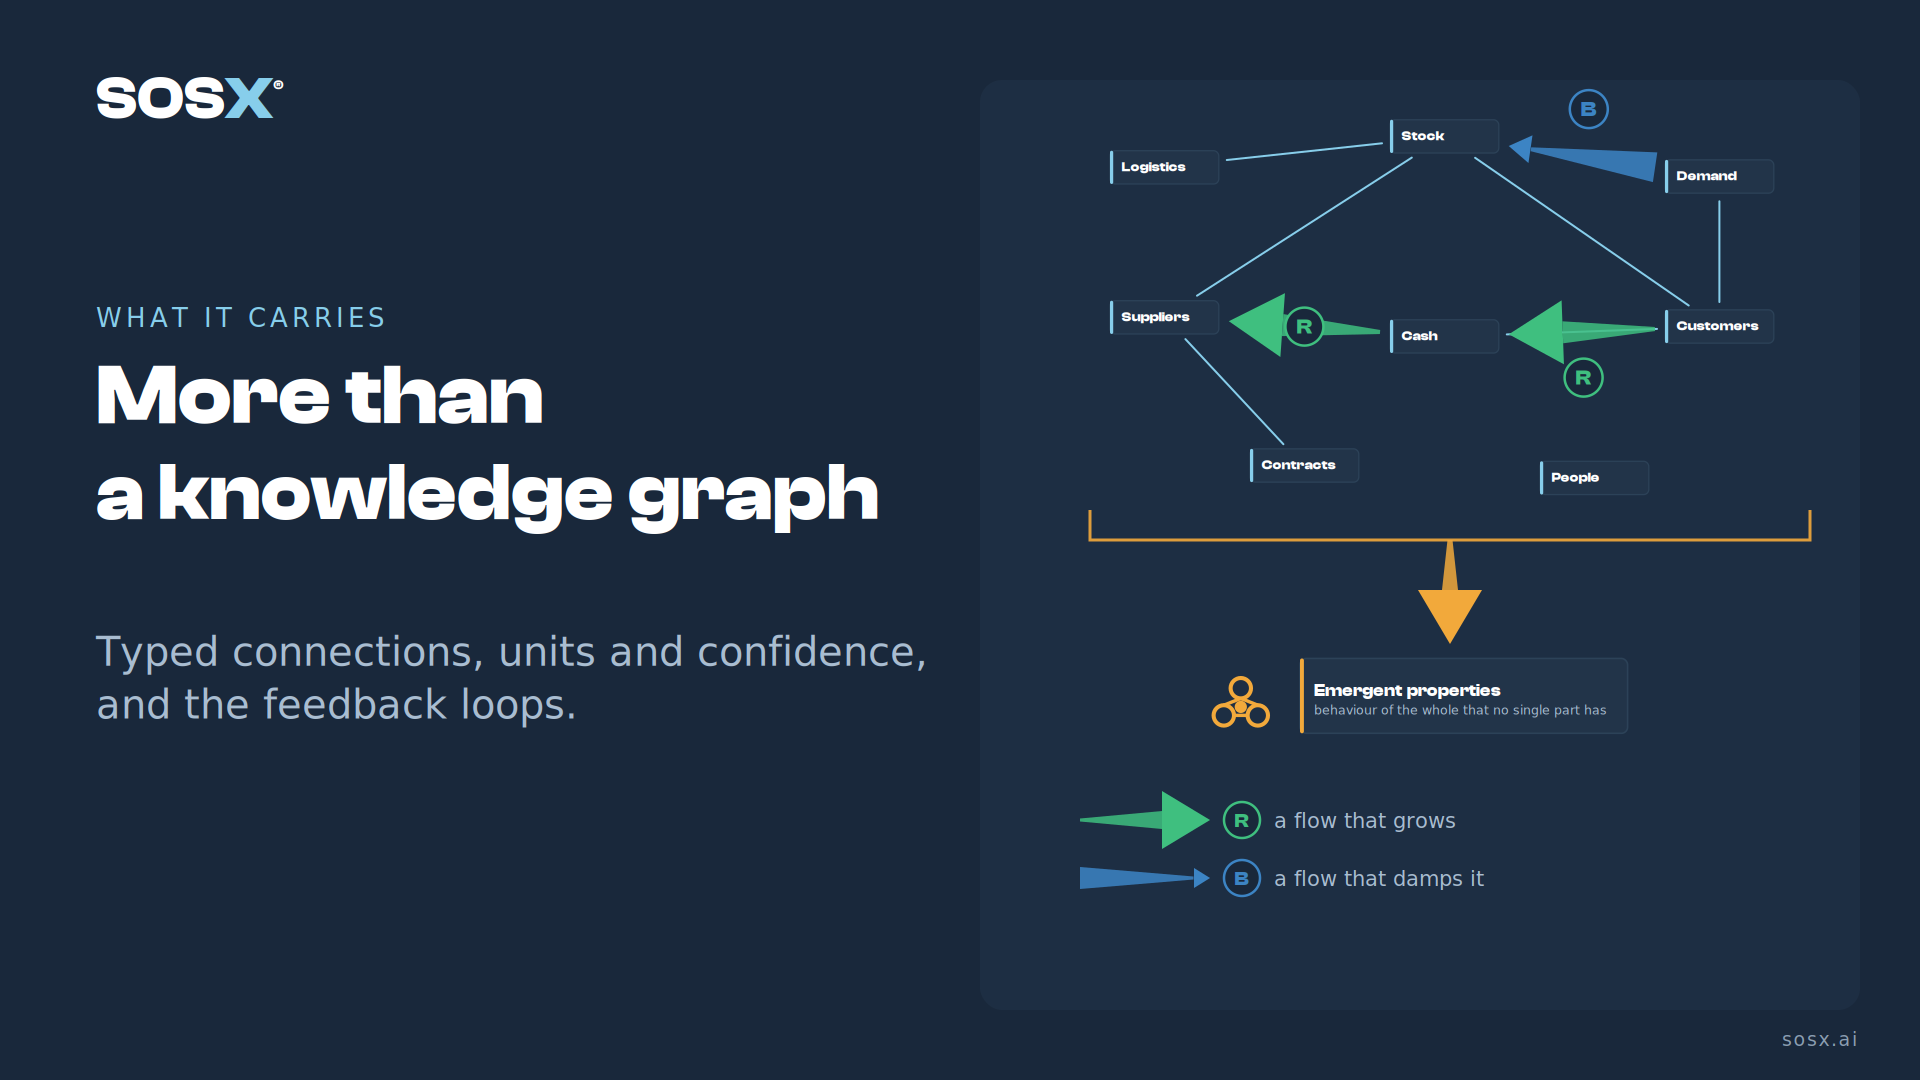 From first principles
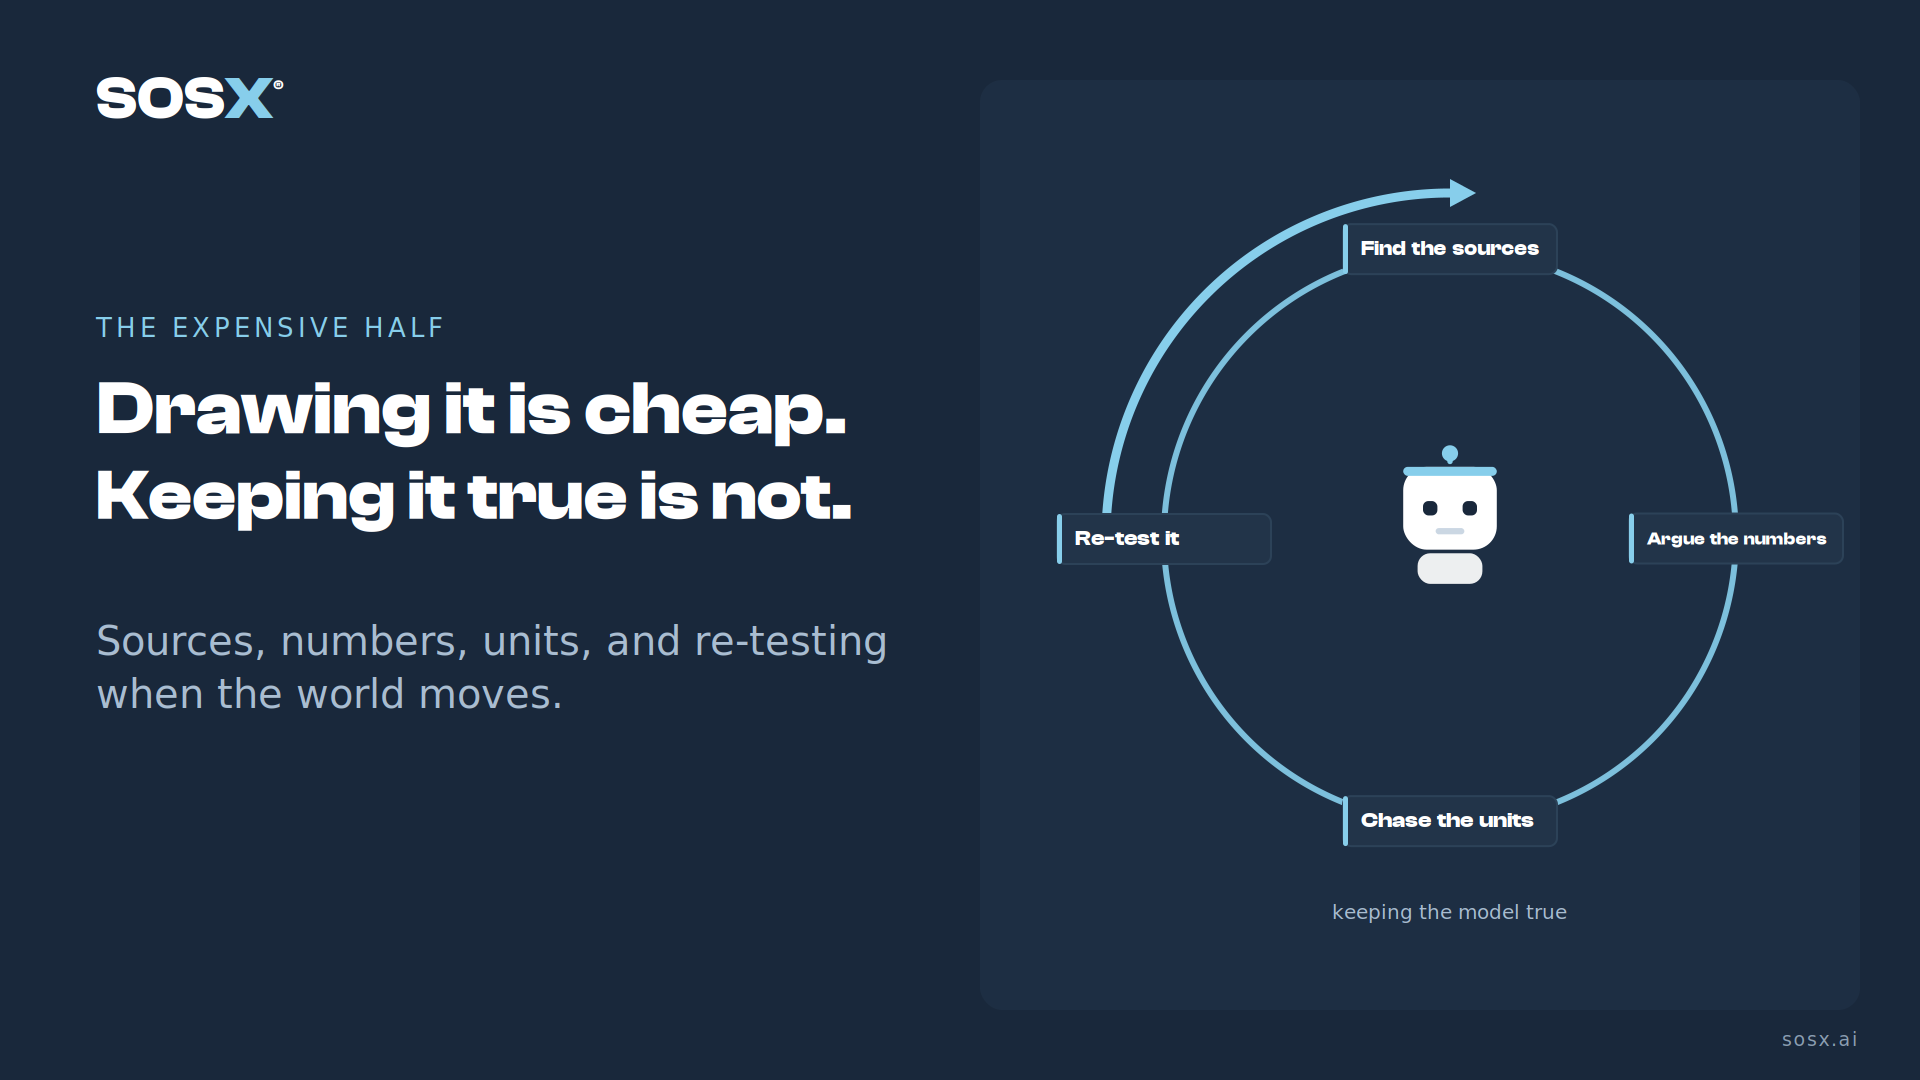 The discipline first
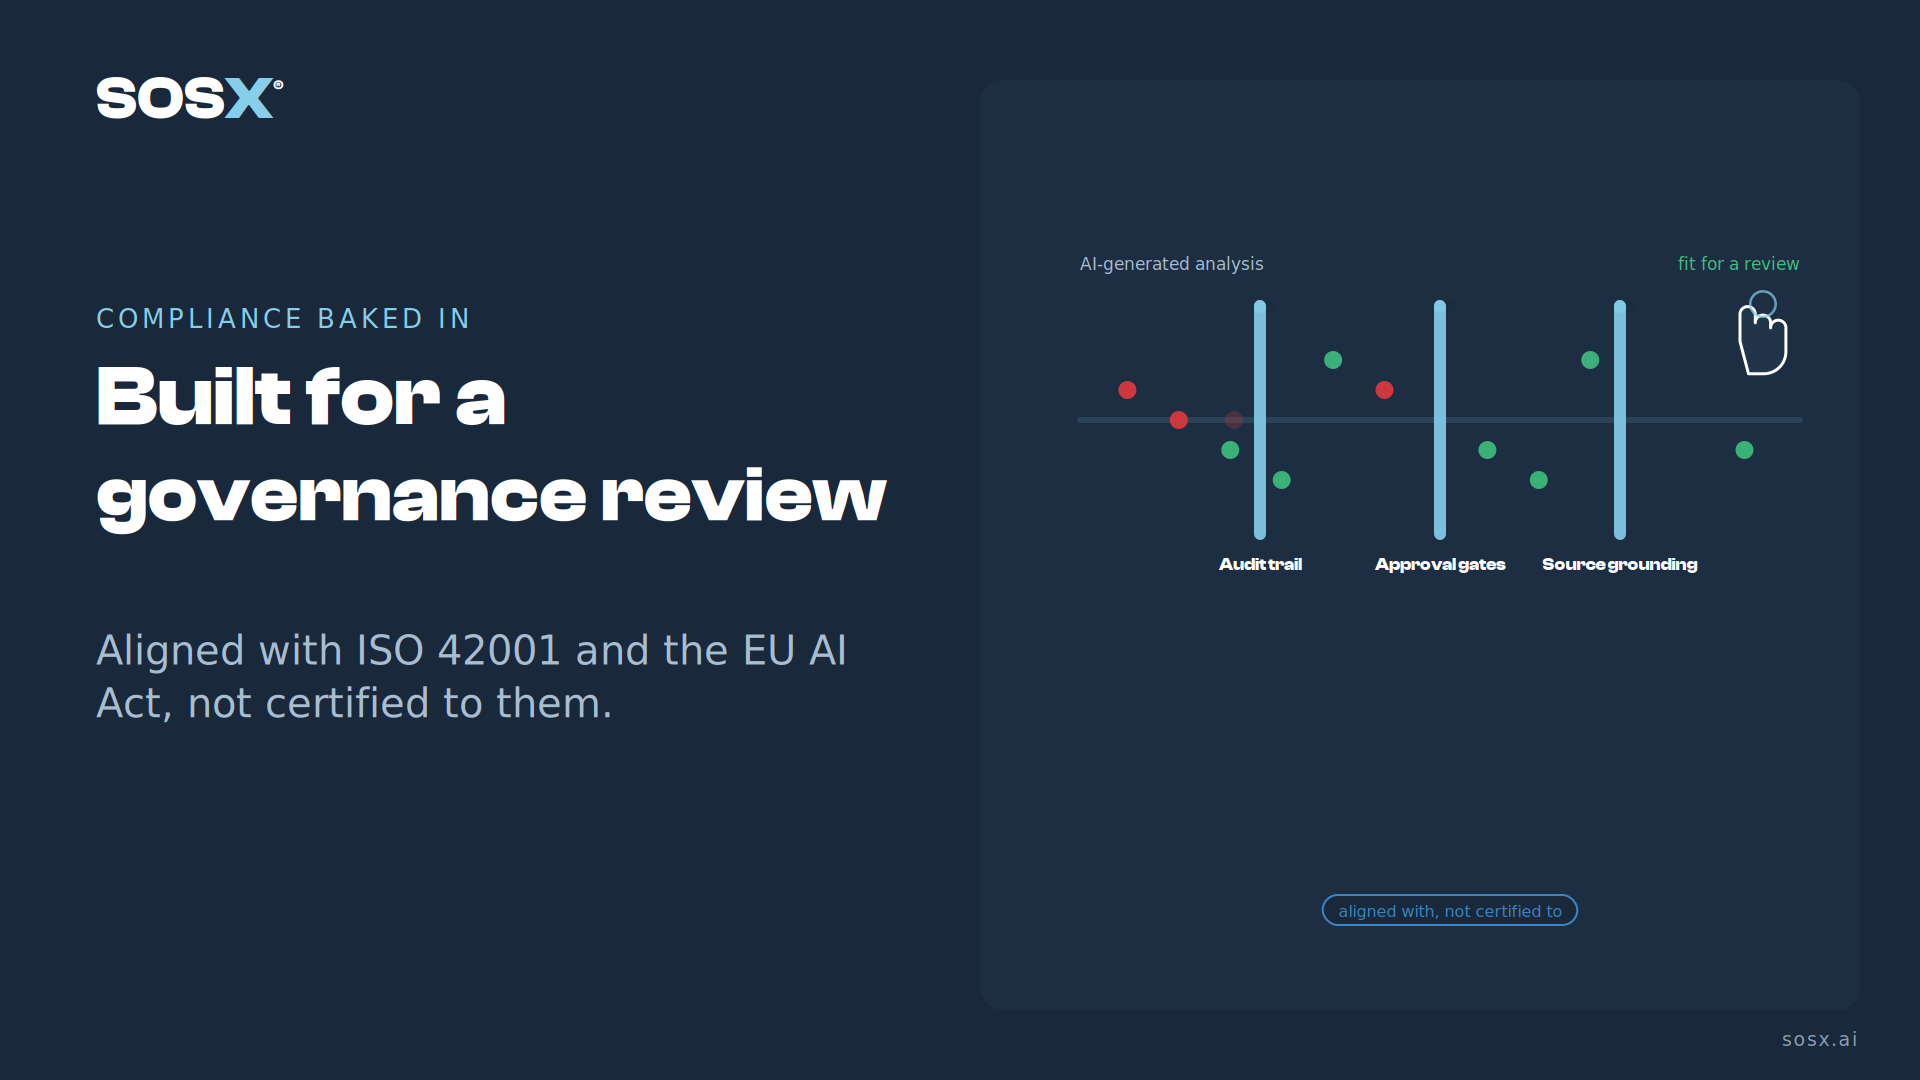 Trust you can check
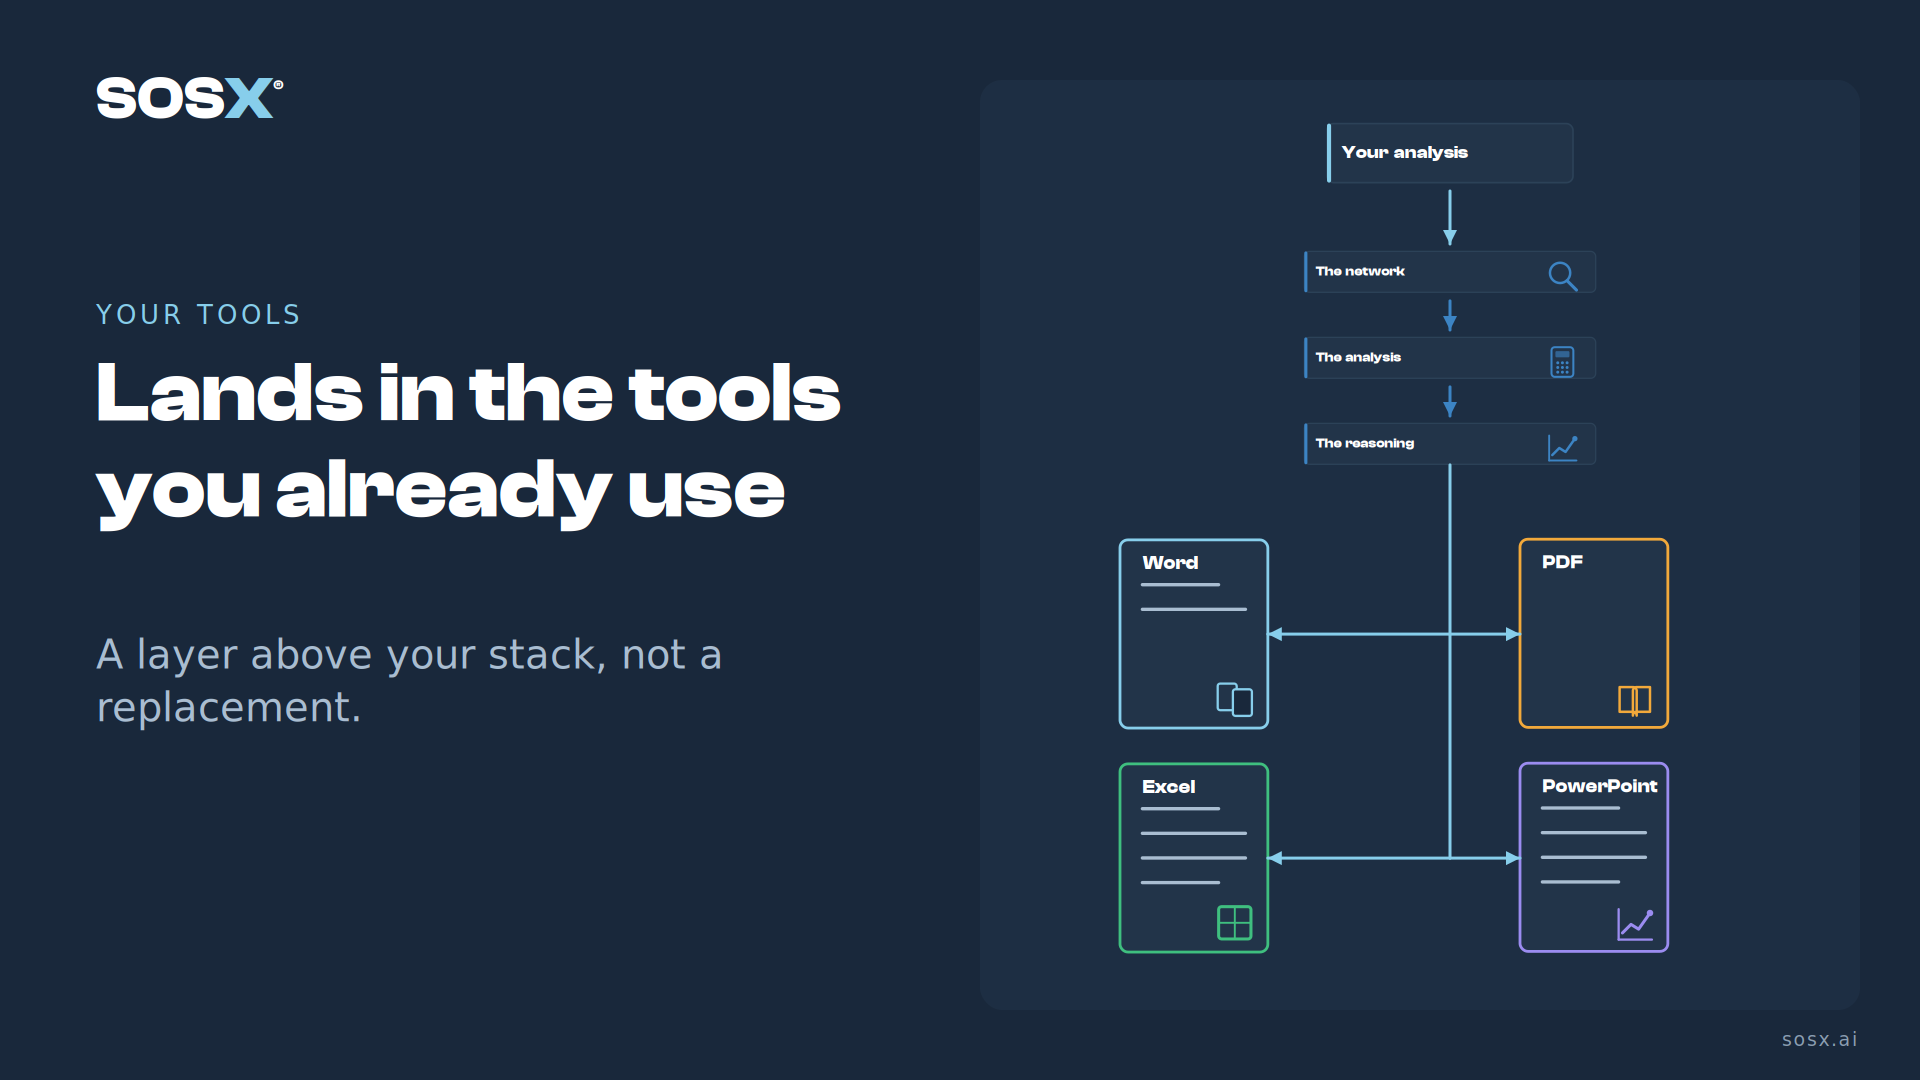 Fits how you work
 Where SOSX comes from
 SOSX at World Summit AI